Melbourne · 17 March 2027 · Collins Square Events Centre
Short, sharp and interactive: keynotes and case studies from practitioners, live panels you vote in, peer roundtables on the problems you name, and two hours of structured networking by design.
All times AEDT. Speaker lineup and agenda announcement coming November 2026. Sign up for the full lineup drop announcement below!
Beat the rush and join us early for complimentary barista-made coffee and breakfast.
Kick off the day with a welcome from your MC and a look at what's ahead.
MFA can work exactly as intended and the account can still be compromised. Once a user has authenticated, attackers can target the session, token or browser state created afterwards and use it without going through the login process again.
This session looks at how one organisation is protecting access after authentication succeeds, how quickly stolen sessions can be identified and what has to happen when a trusted session suddenly becomes untrusted.
We'll cover:
With Australia's Digital ID system now opening to the private sector under the Digital ID Act, organisations face a genuine strategic choice: become an accredited relying party, wait, or build alongside. This keynote unpacks where the rollout actually stands, the accreditation and cost realities of myID and the AGDIS, and how leading organisations are turning verified digital identity from a compliance obligation into a trust and onboarding advantage.
Identity now sits in front of almost everything employees need to do. If a core identity platform is compromised or unavailable, recovering the rest of the business can depend on getting identity working first.
This panel looks at how organisations prepare for an identity outage or compromise, what needs to be recoverable first and whether their plans would actually work under pressure.
We'll discuss:
Authentication answers who someone is. It does not necessarily answer whether they should be allowed to perform a particular action against a particular resource at this moment.
This session looks at how organisations are moving away from access decisions buried inside applications and towards policies that can make more specific decisions based on identity, context and risk.
We'll cover:
Recharge with refreshments and structured networking with your peers.
A hands-on, interactive session working through a real identity and access scenario as a room. Details announced soon.
One permission may look harmless. Several permissions connected across Active Directory, Entra, cloud platforms and applications can create a route to something far more powerful.
This session looks at how one organisation mapped those connections, found paths an attacker could use to move from an ordinary identity to critical access and decided which ones to remove first.
We'll cover:
Passkeys and phishing resistant authentication make stealing a password far less useful. That does not mean every route into the account has disappeared.
This session looks at what happens after organisations strengthen the login and attackers start targeting weaker fallback methods, authenticator enrolment, new devices and account recovery instead.
We'll cover:
From 15 March 2027, public TLS certificates max out at 100 days. That turns certificate renewal from an occasional operational task into a continuous automation problem and exposes the wider issue of how organisations discover, own and rotate machine identities at scale.
This panel looks at how organisations are automating certificates and other machine credentials before shorter lifetimes make manual processes unmanageable.
We'll discuss:
Small-group, discussion-based sessions where you'll work through real identity and access challenges with peers in similar roles. Roundtable topics will be announced soon.
Enjoy a complimentary lunch while connecting with fellow attendees.
Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights (and a travel voucher) as the top scorer takes the crown.
Strong authentication does not help if an attacker can persuade a service desk to reset MFA, enrol a new device or recover an account.
This session looks at how organisations are tightening the human side of identity recovery and what evidence should be required before somebody is given control of an account again.
We'll discuss:
Permanent privileged access is convenient, but it also means powerful permissions are sitting there whether somebody needs them or not.
This session looks at what it takes to replace standing access with temporary privilege, how organisations handle emergency and overnight access and what happens when security controls meet the reality of administrators and developers trying to do their jobs.
We'll cover:
Large identity environments rarely look the way anyone would design them today. Years of mergers, platform changes, legacy applications and point solutions leave organisations running multiple identity providers, directories and authentication methods at the same time.
This think tank puts that reality to the room, panelists and audience together, to work through what should actually be removed, replaced or tolerated if organisations had the chance to simplify the identity environment now.
Questions we'll cover:
Wrap-up of the day's key takeaways, and your chance to win some epic prizes.
Unwind with your peers for a couple of drinks on us!
See you at Identity World New York on May 6, 2027.
Short, sharp and interactive by design. No slide-after-slide days.
Solo stage time from a practitioner or an invited expert, framing where the discipline is heading.
Three or four leaders comparing programmes directly, moderated to stay concrete rather than abstract.
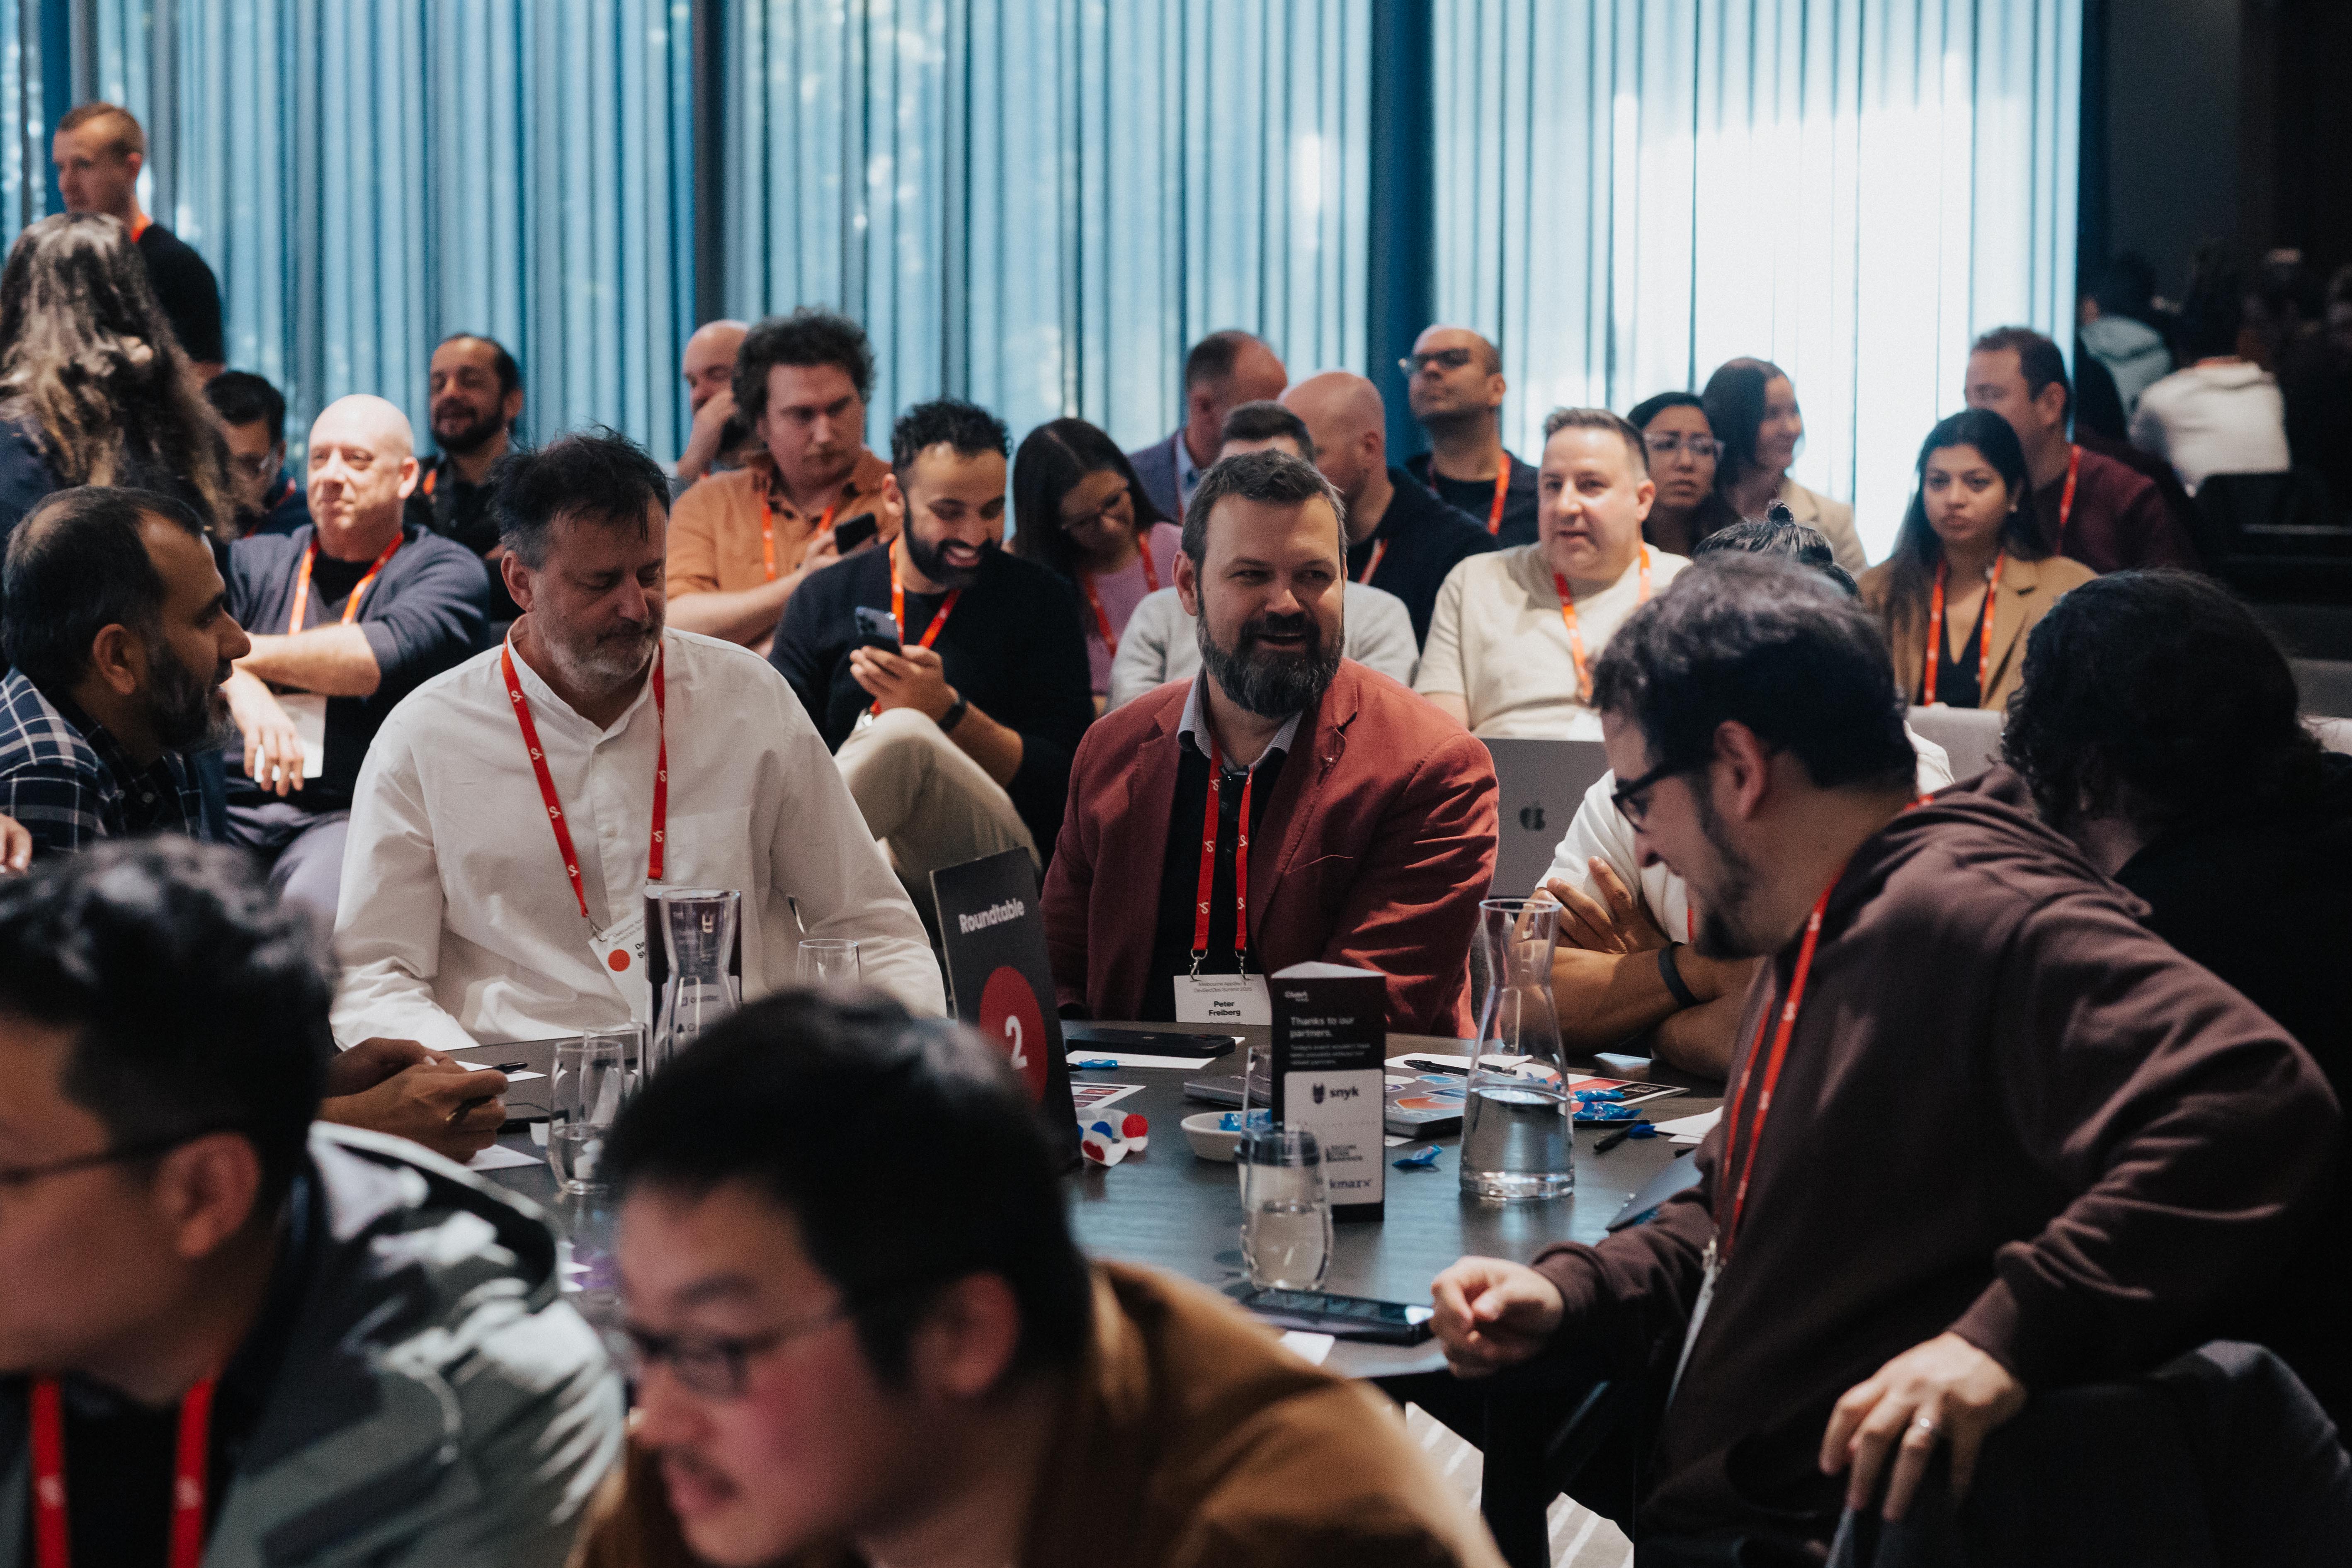
Small-group peer discussion on a single named problem, with no audience and no slides.
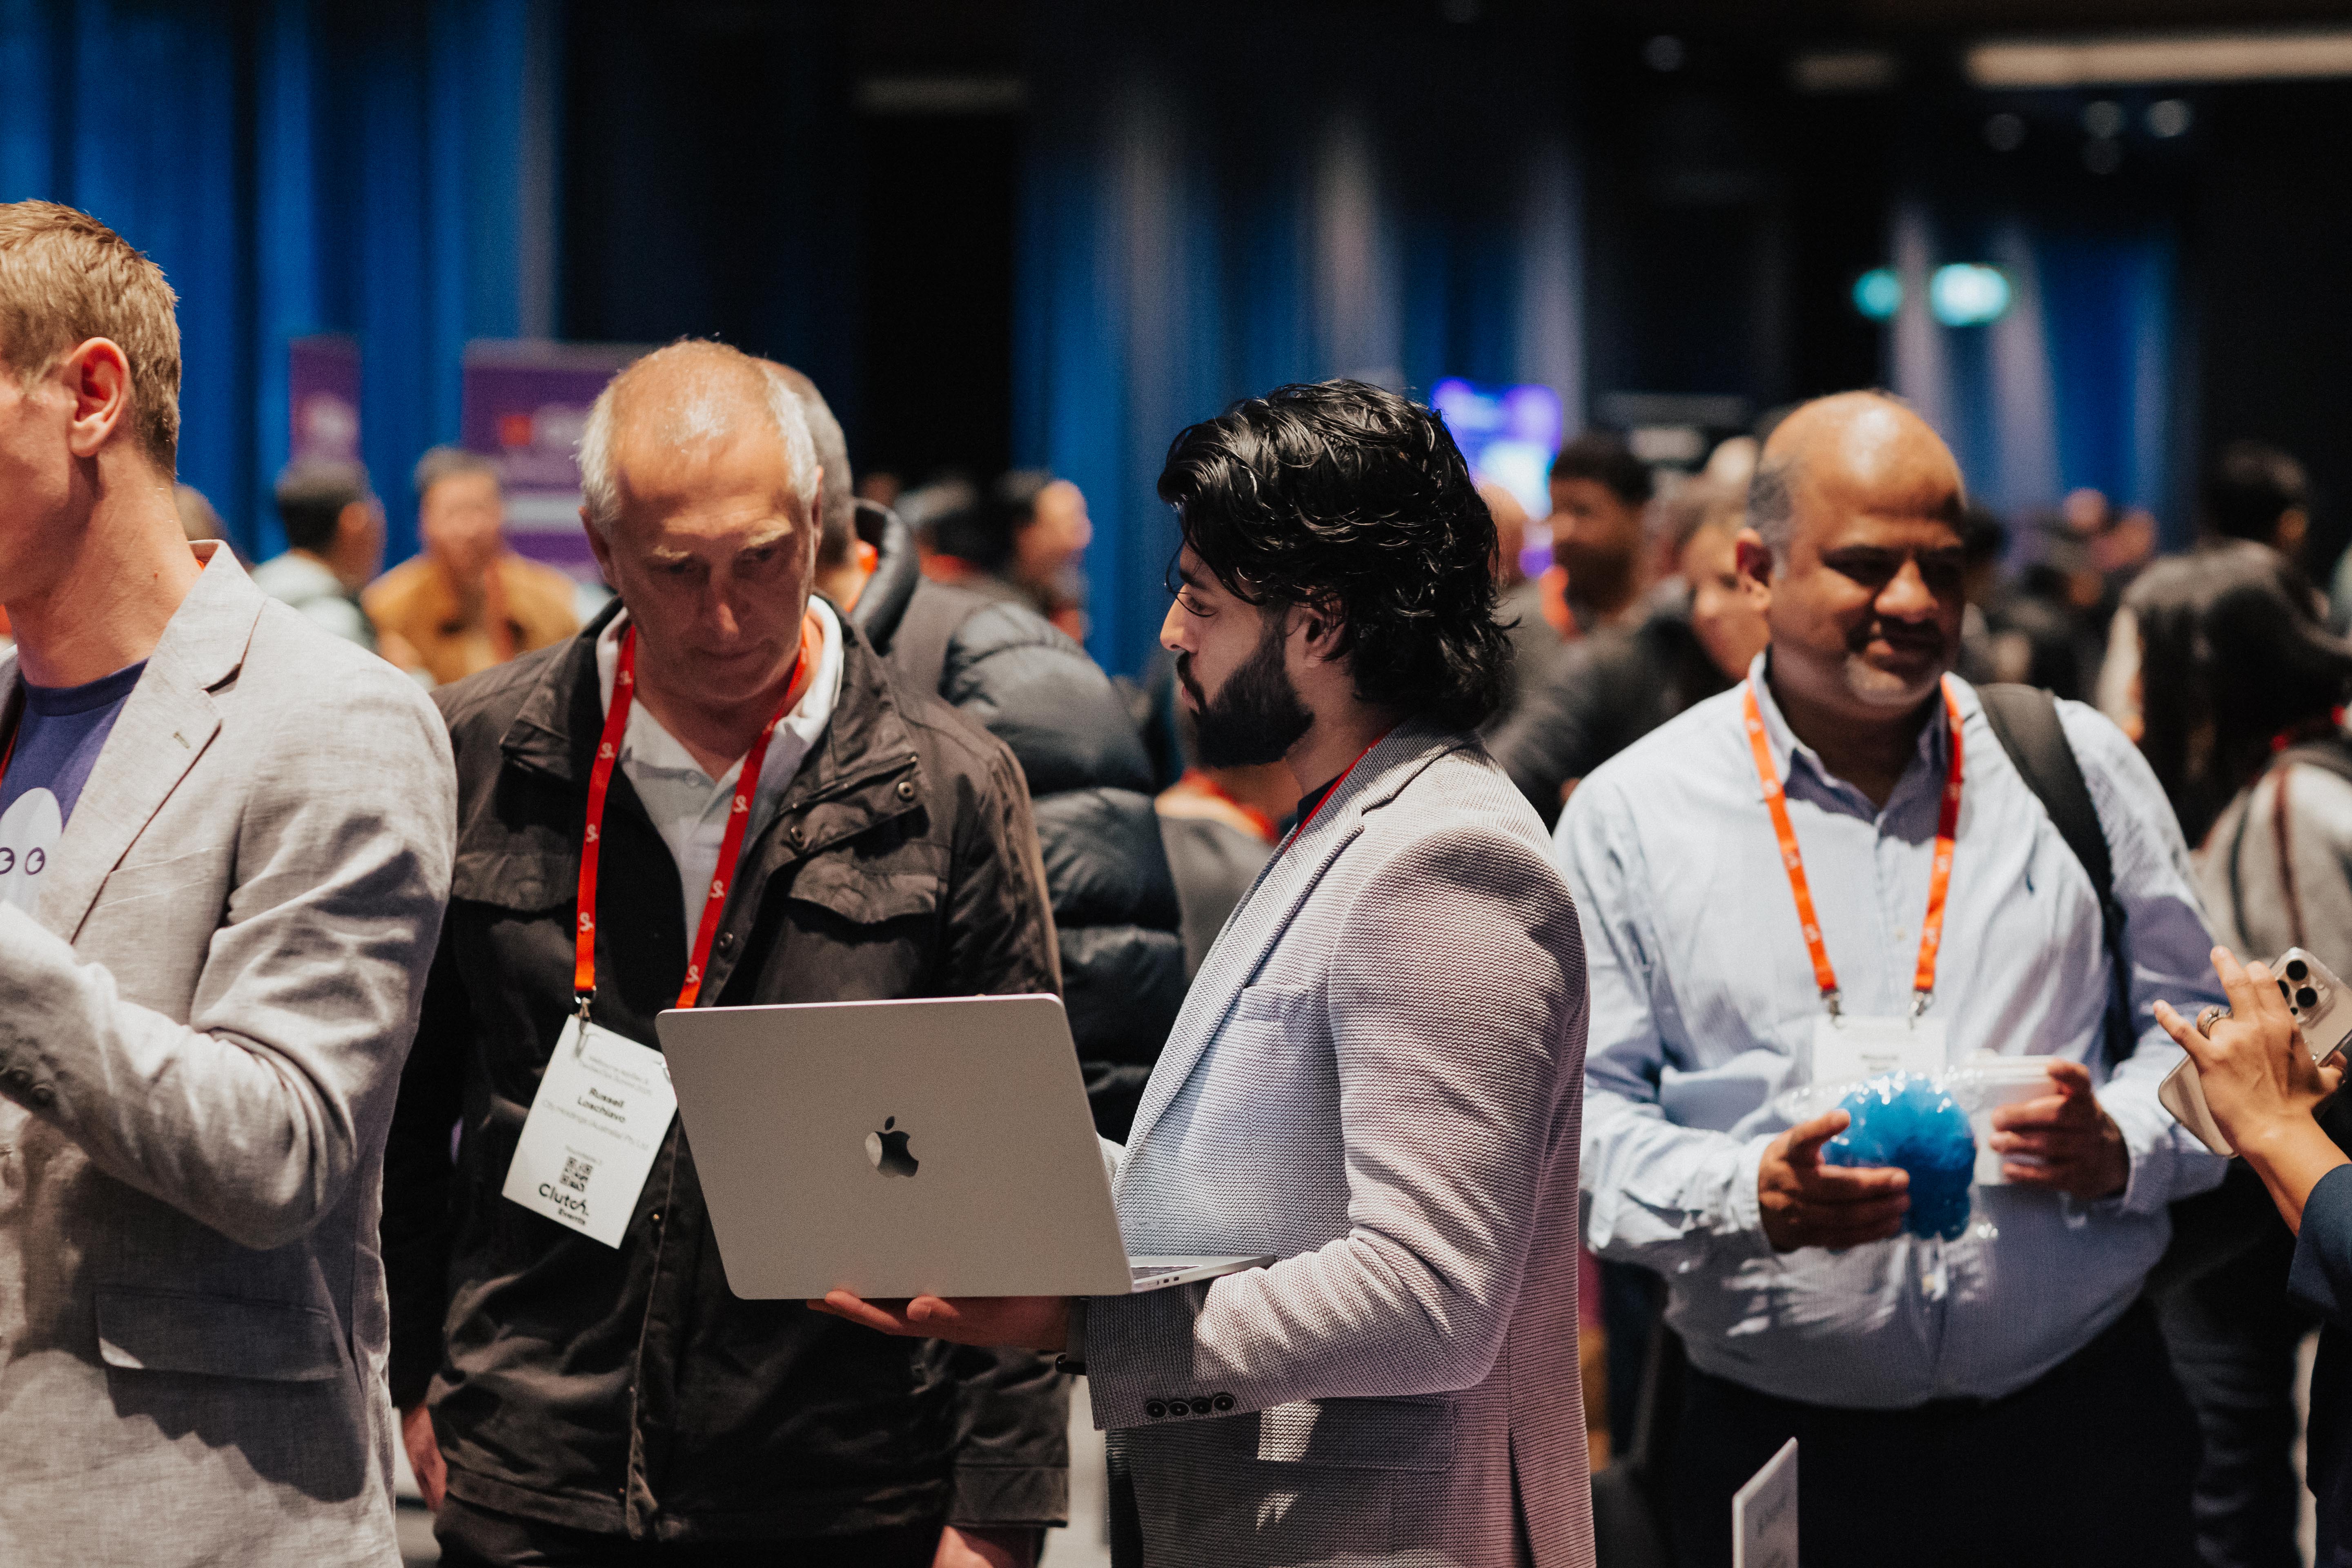
Curated, opted-in meetings between practitioners and the partners they choose to meet, scheduled around the programme so nobody misses a session.
Two hours of the day given to breakfast, lunch and drinks by design, so the conversations started in the room carry on outside it.
Global perspectives on identity and digital trust featuring localised experts and region-specific, tailored agendas curated by IAM leaders facing the same challenges as you.